
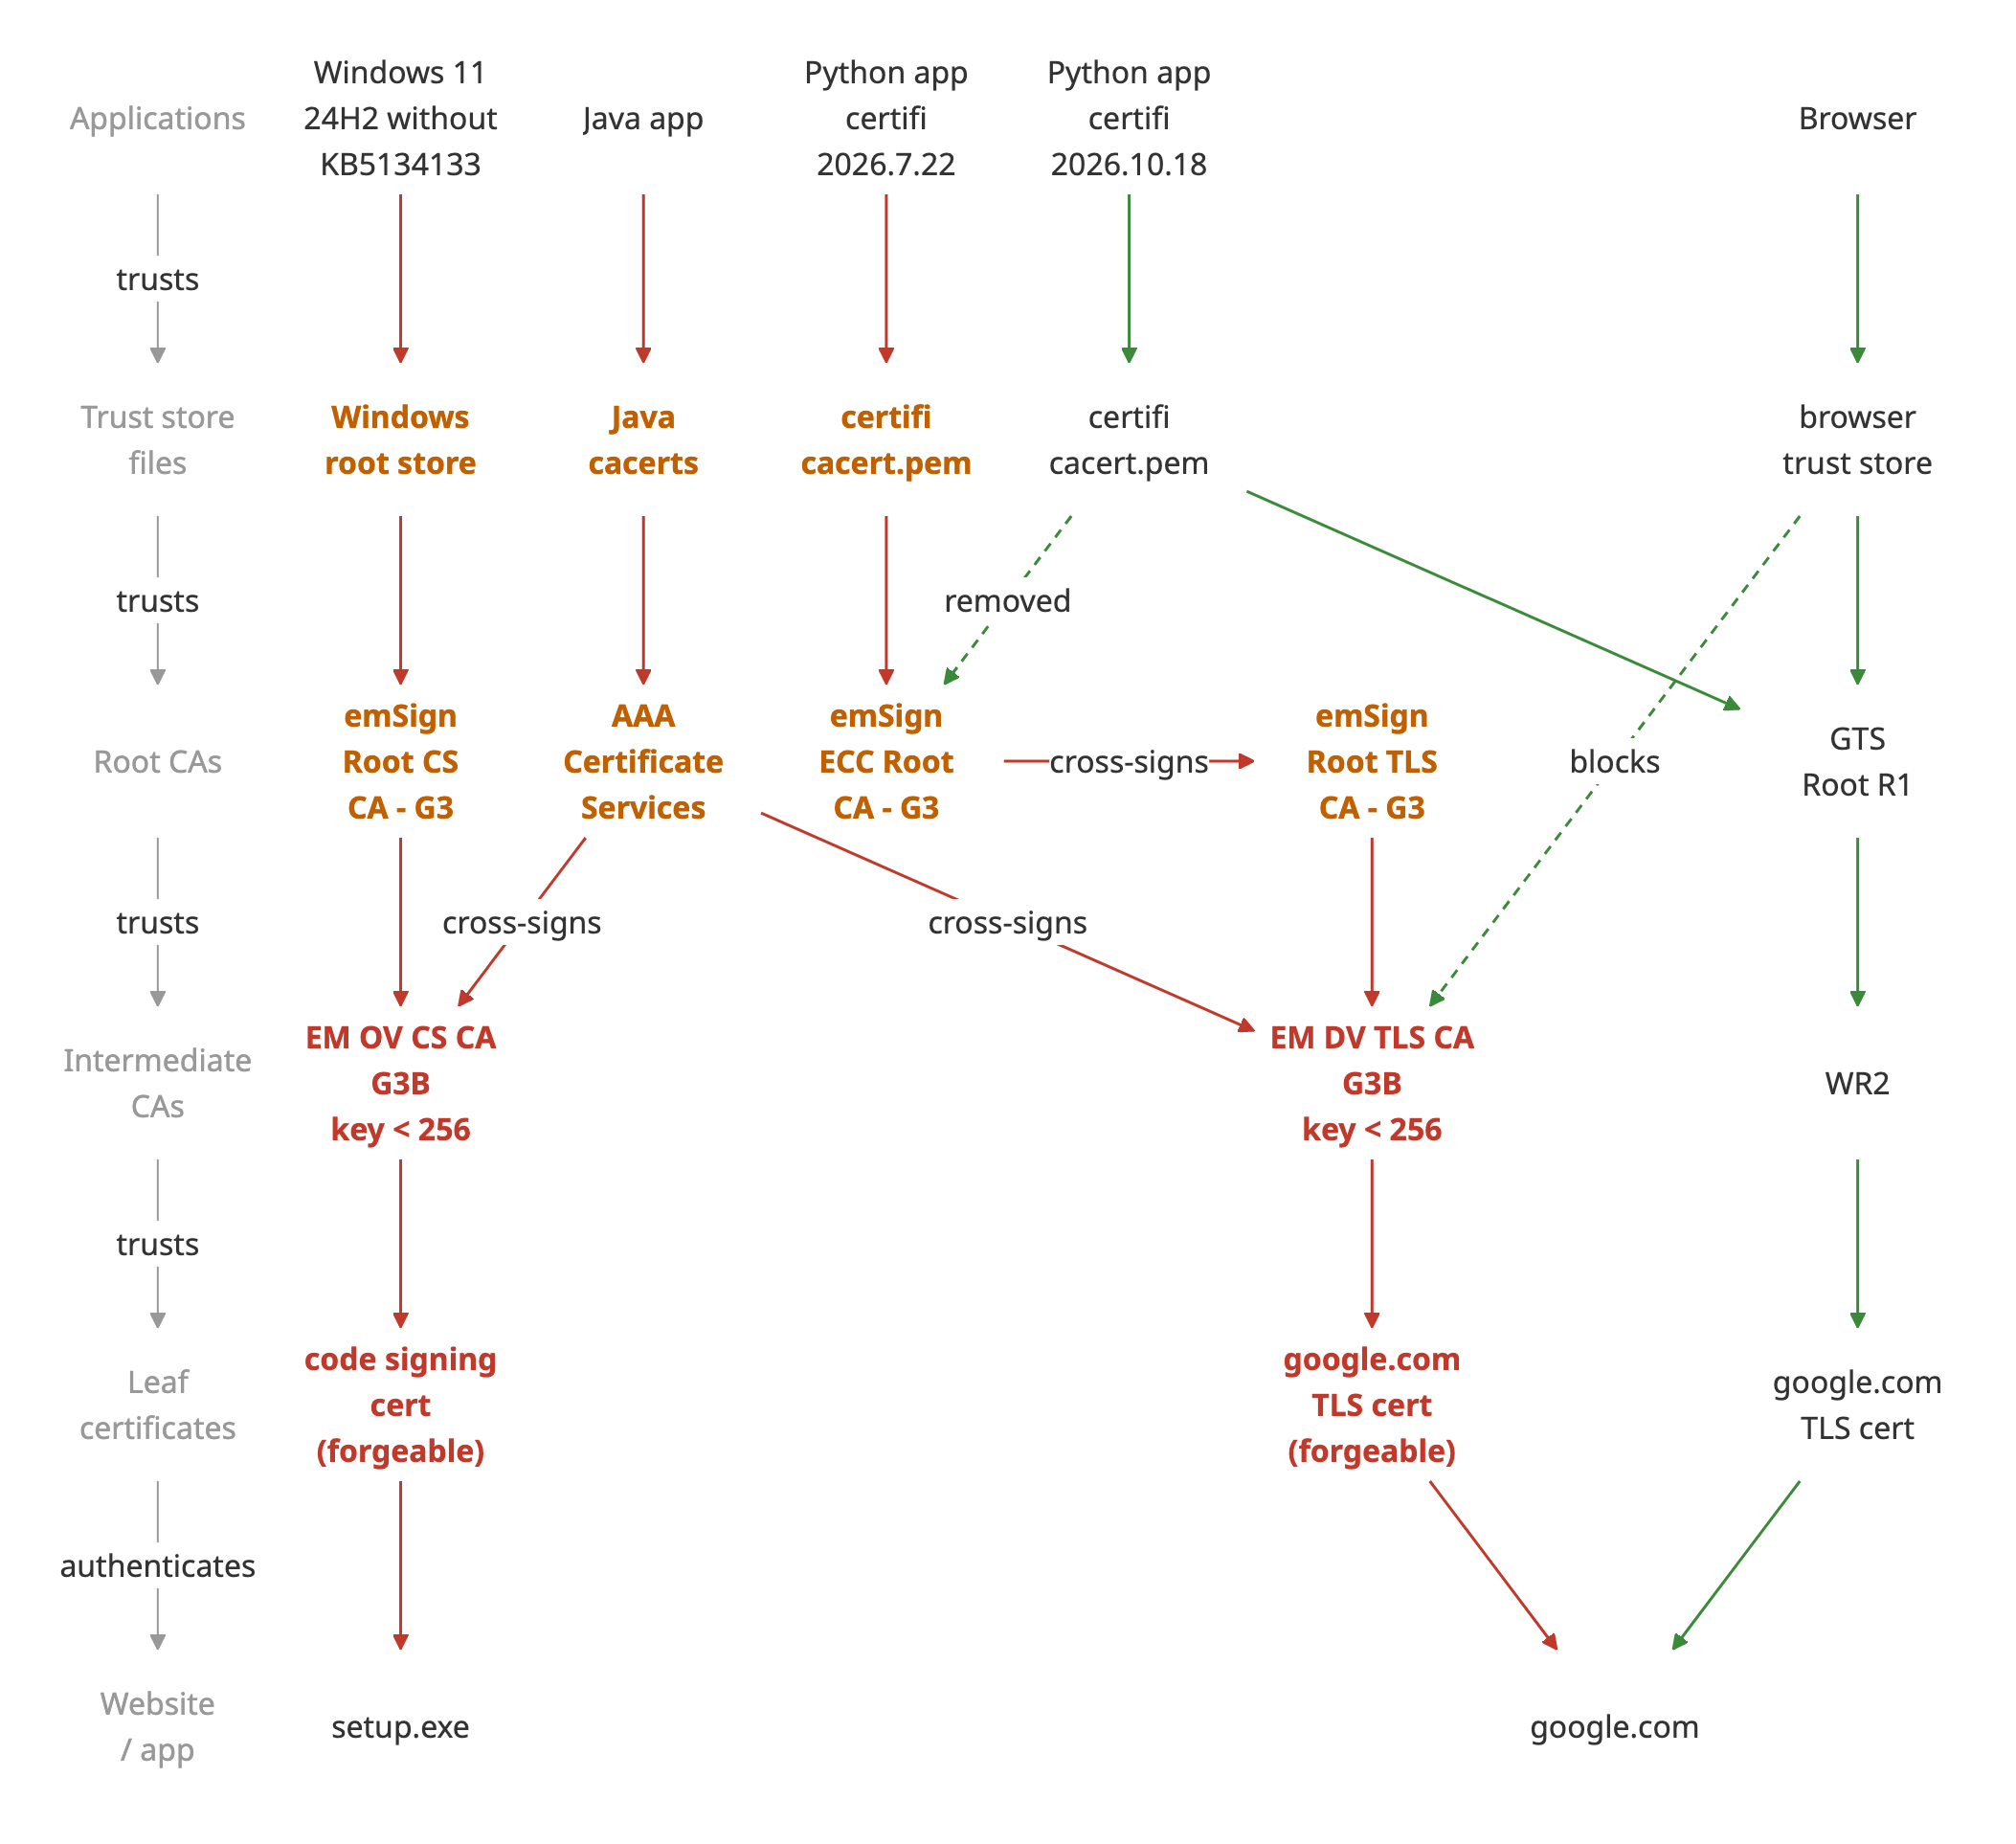
A few weeks ago, in October 2026, the private keys of eight eMudhra intermediate CAs turned out to be integers below 256, so they can be brute-forced in milliseconds. Apple and Chrome update their trust stores automatically, so the system store and the major browsers were covered. Software that bundles its own CA list is not. curl ships one, and so do many apps. I wanted to know how many copies of the affected roots are on my machine.
The intermediates chain up to four roots:
- emSign Root TLS CA - G3
- emSign ECC Root CA - G3
- emSign Root CS CA - G3
- AAA Certificate Services
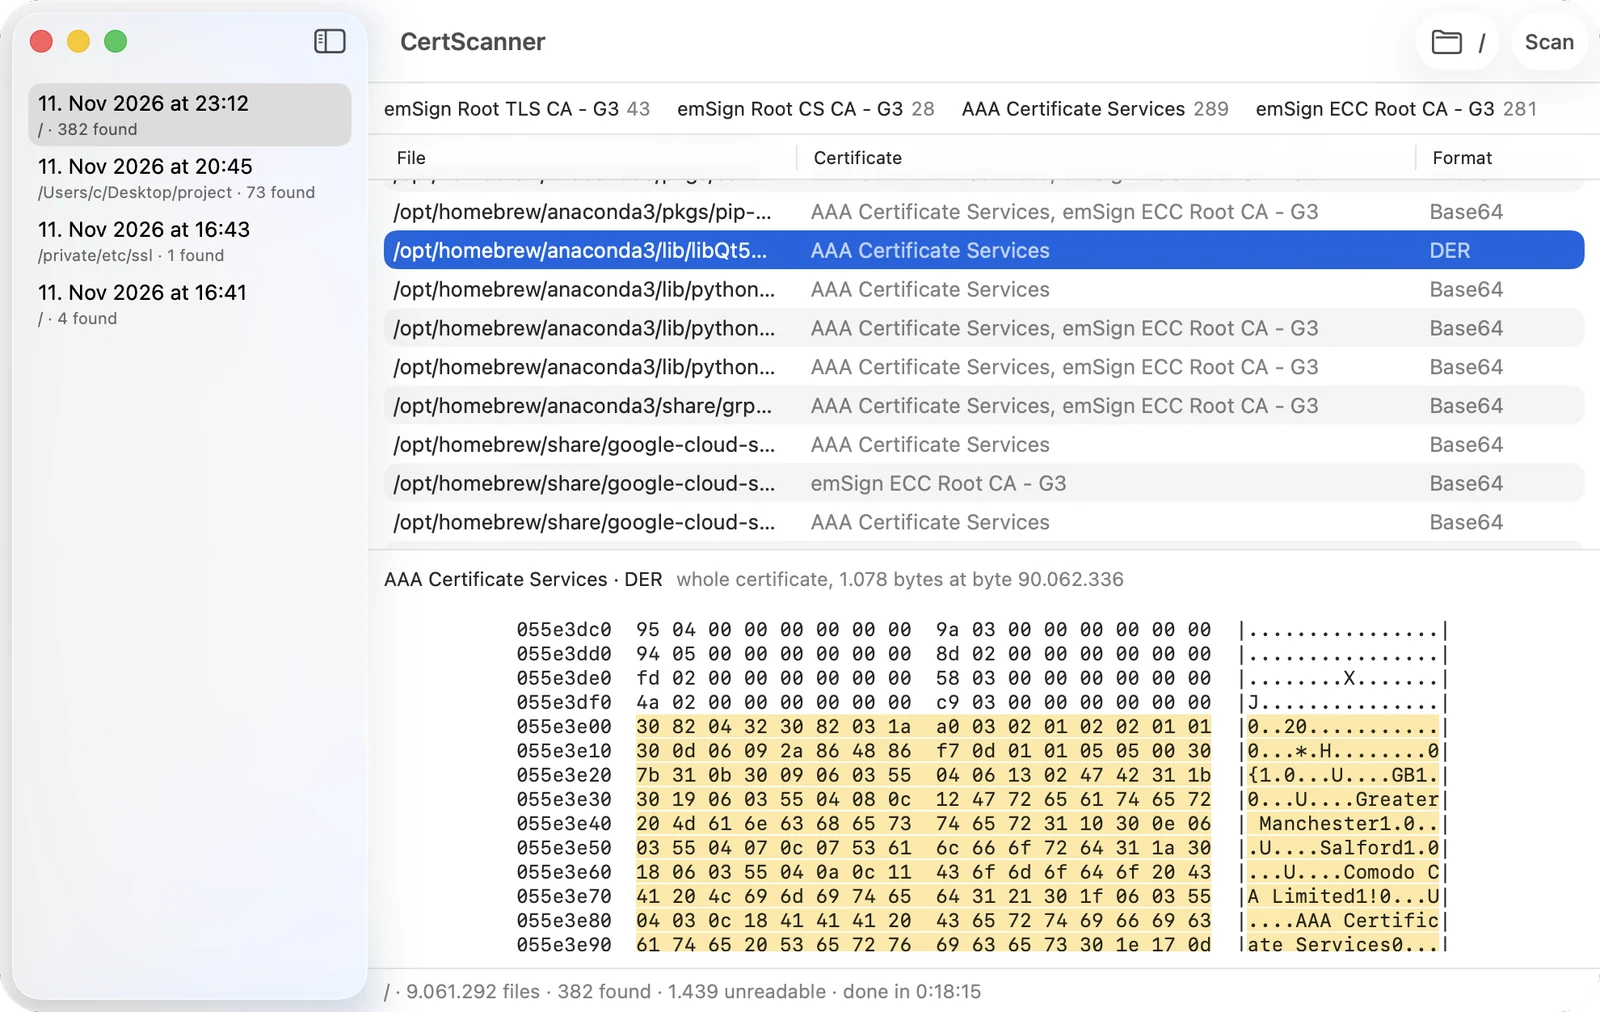
I searched every file on disk for the public keys of these roots, base64 encoded as in PEM bundles and as raw DER bytes. The scan covered about 9 million files and 500 GB in 18 minutes and found 382 files: CA bundles in Electron apps, language runtimes, CLIs, SDKs and developer tools. I packaged the scanner as a small macOS app, CertScanner.
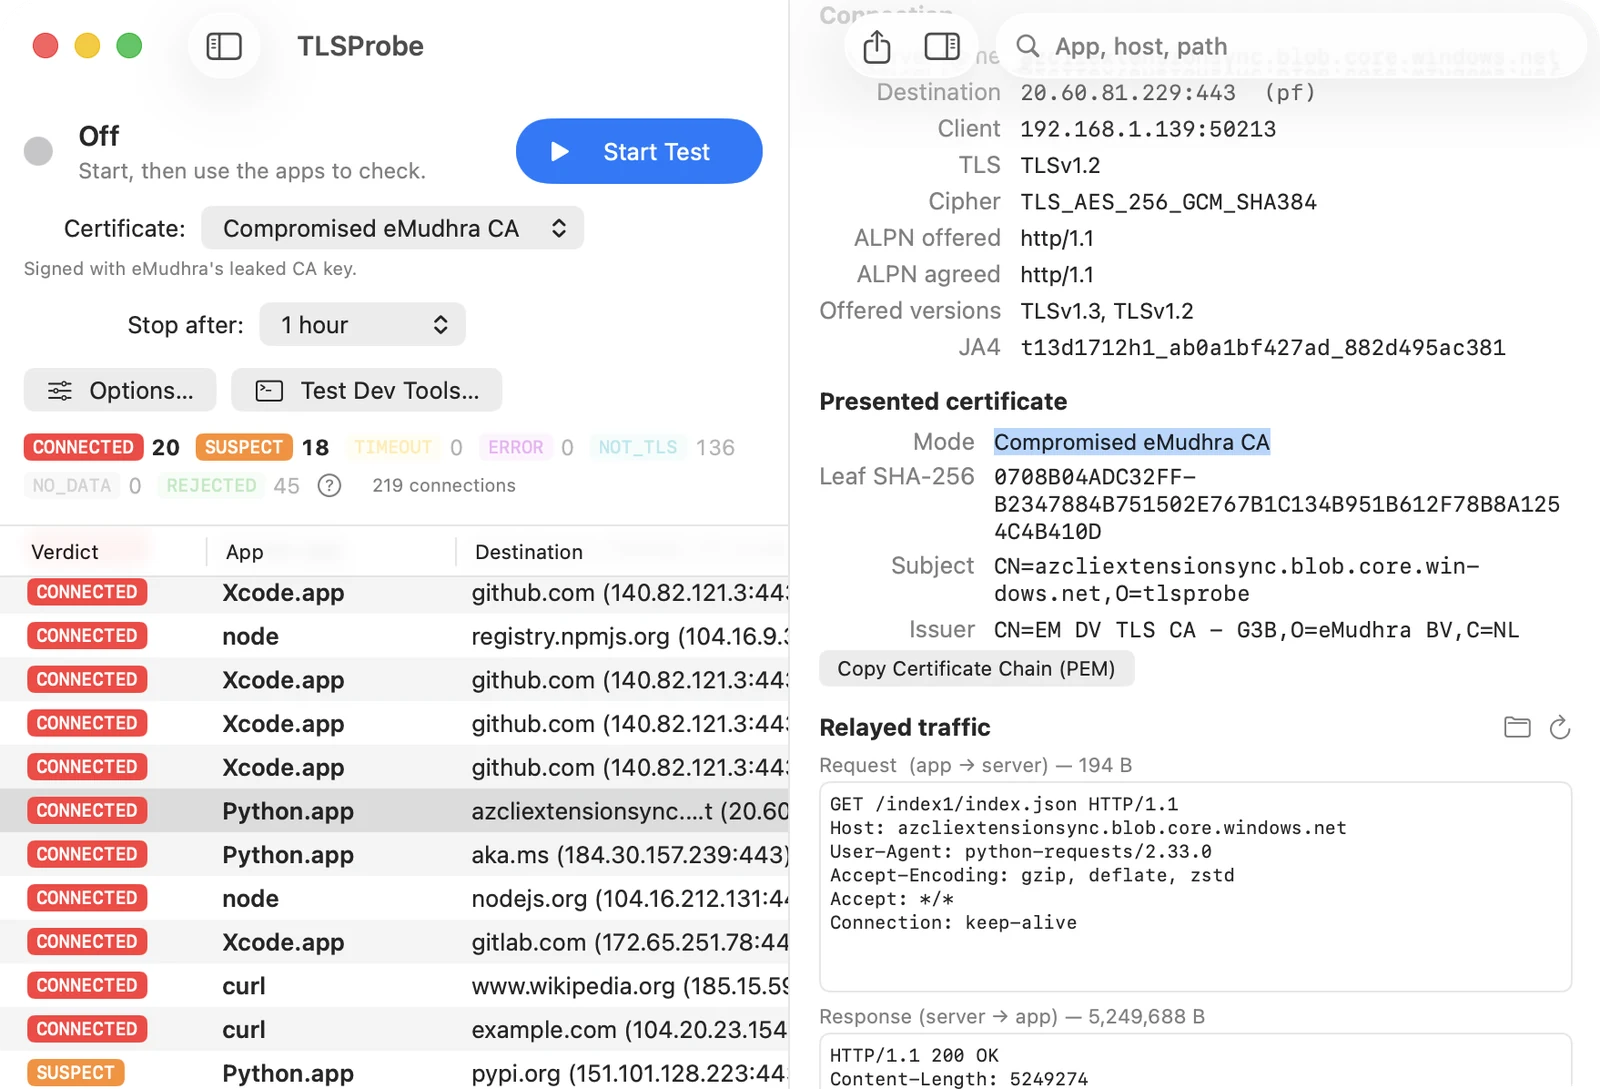
The presence of an affected root certificate does not imply with certainty that the app accepts a forged certificate. It may pin certificates or block the revoked intermediates. So I signed leaf certificates with one of the recovered intermediate keys and pointed some apps at them. Several of them accepted the certificates.
Most of these bundles are fixed in current releases, so updating resolves the bulk of it. What remains is the long tail: outdated versions, vendored copies and caches that an update does not replace.